
Google DNS server in my Kindle configuration, seriously?
While configuring my Kindle network settings, I observed something spooky. Despite using DHCP and my own network services, there appeared the Google DNS server address 8.8.8.8 in the network configuration, always.
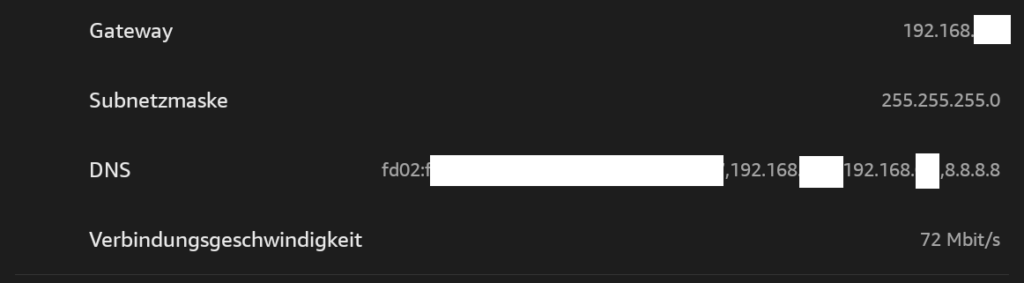
After doing some research on the Internet, I’m not alone!
E.g.: Kindle Fire HD 10 9th gen is adding a dns server on its own. | XDA Forums (xda-developers.com)
Well, think about this: Although I provide my own network and DNS server configuration using DHCP, the Google DNS server appears in the Kindle configuration, always!
I’m not amused! This is an attack on a sovereign state!
For a good reason, I make use of my own DNS server. We do have a wide range of tablets and media devices in my family. And my kids start to make use of them.
Therefore, I’ve implemented a DNS server, based on the Pi-hole project. E.g. Pi-hole will enable me to define allow- and deny lists, using regular expressions. E.g. this will give me the freedom to control unsafe content, block ads and chatty devices. And there are many more good reasons to provide your own DNS server.
Always providing a foreign DNS server in the network configuration is unacceptable!
How to get this sorted?
Based on discussions on the Internet, there’s no easy way to remove the configuration. And maybe, on the next update or upgrade the configuration will reappear. I have a large number of different devices, I need a centrally managed solution.
Thankfully, I have a core router with advanced functionality. Maybe, my other post about black hole routing came to your attention? In the mentioned post, the solution is perfectly described.
I configured my core router to send all requests targeting Google DNS servers into a black hole route, effectively sending them to /dev/null.
set protocols static route 8.8.4.4/32 blackhole distance 1
set protocols static route 8.8.8.8/32 blackhole distance 1
set protocols static route6 '2001:4860:4860::8844/128' blackhole distance 1
set protocols static route6 '2001:4860:4860::8888/128' blackhole distance 1
Bye-bye! Google DNS server…
A good summary of black hole routing syntax for BSD, Linux, IOS and Windows is available here: http://blog.up-link.ro/how-to-add-a-nullroute-blackhole-filtering/
Why not use firewall rules?
Yes, indeed! It’s a good idea to block all outgoing traffic on port 53 (TCP/UDP). Except for your own DNS server and forwarder, of course.
Routing is less CPU-intensive than firewalling, and you can’t be sure it will be port 53, always. I chose this way, in addition.
For clarity, this blocks Google Public DNS specifically. It does not block other public DNS resolvers, DNS-over-HTTPS, or DNS-over-TLS. For a stricter DNS policy, combine this with firewall rules that allow DNS only to the local resolver and block or redirect outbound DNS traffic where appropriate. – That may become another blog post.